Loading...
×
close
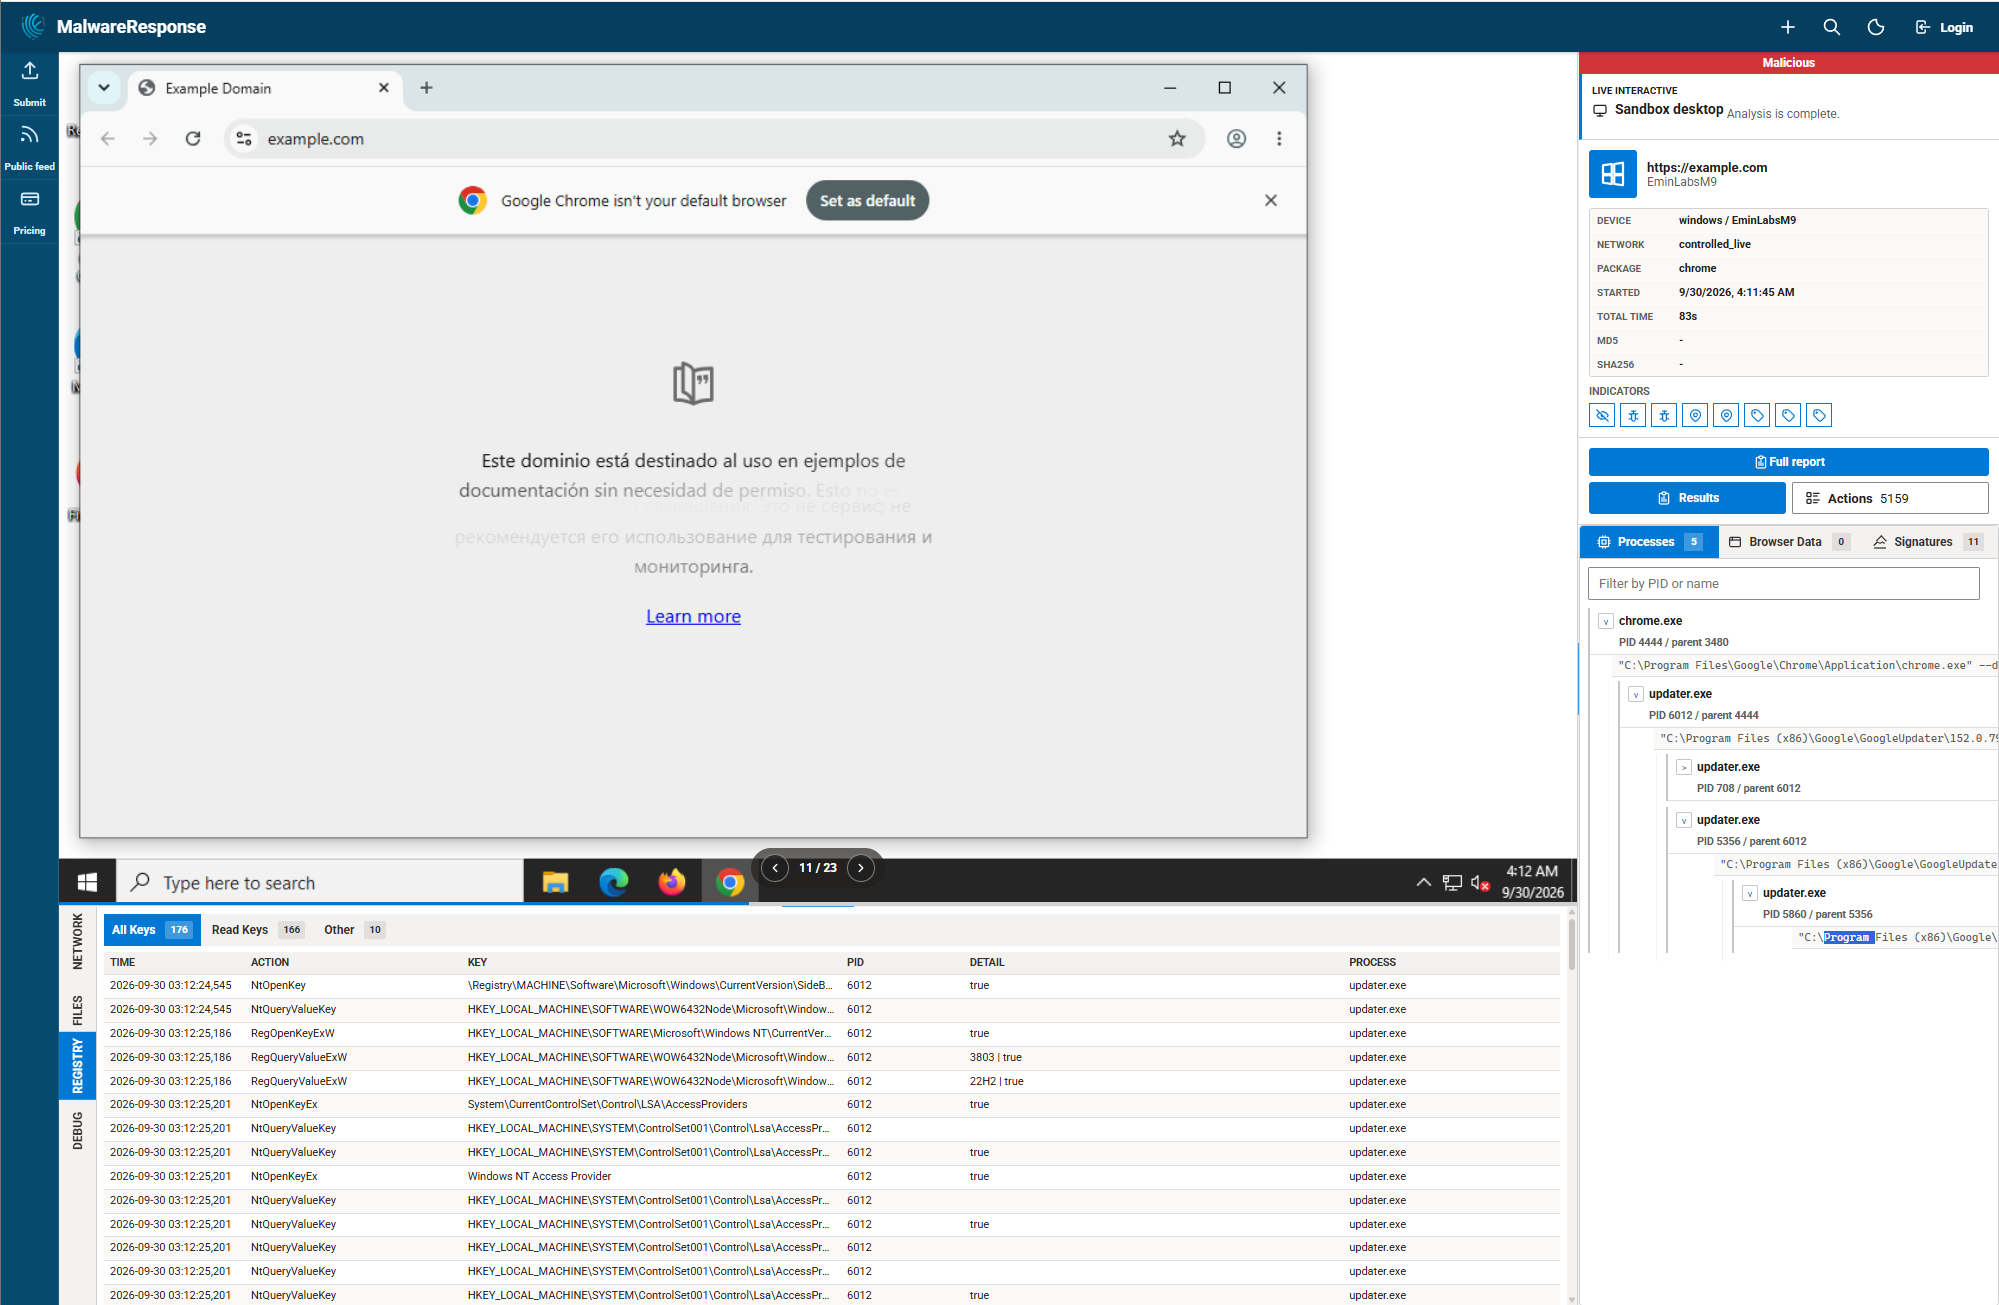
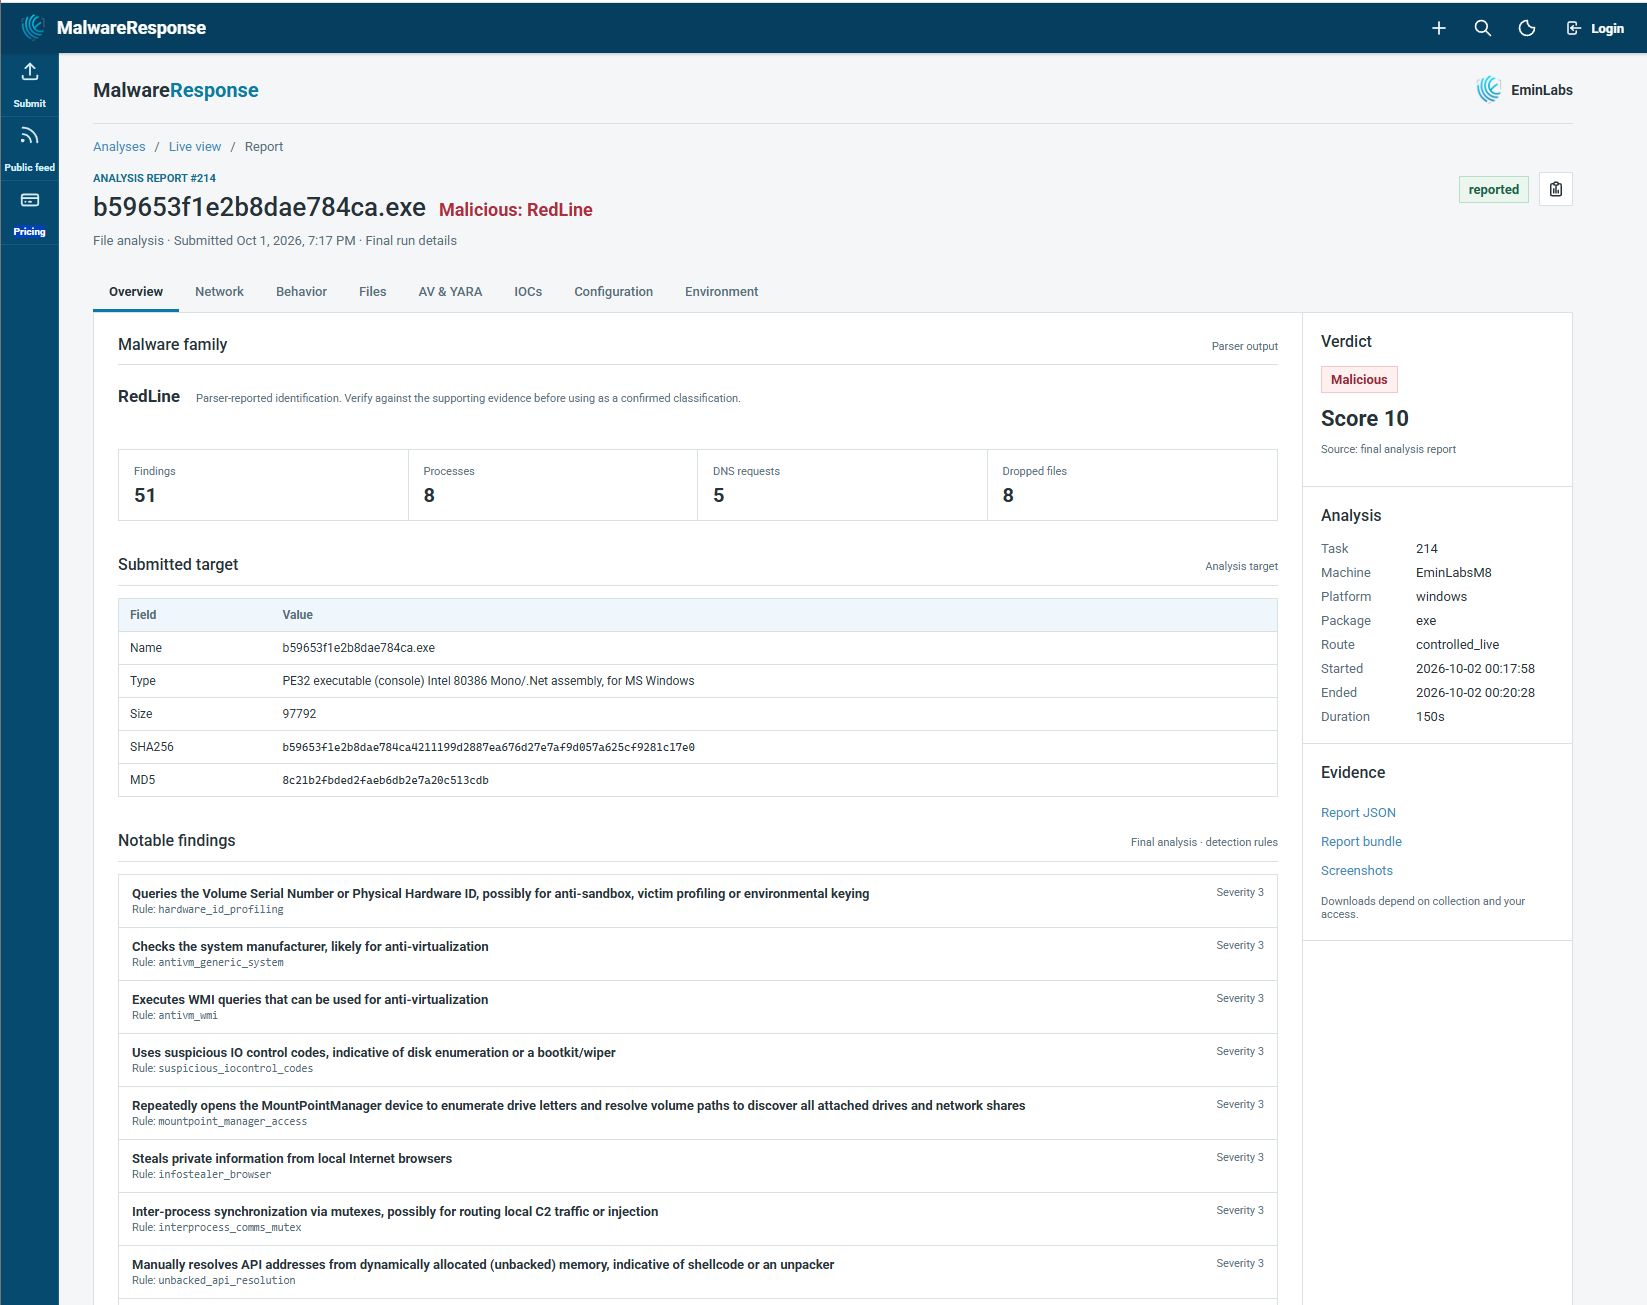
Analyze files, URLs, and malware behavior with response-ready evidence visual

Analyze files, URLs, and malware behavior with response-ready evidence

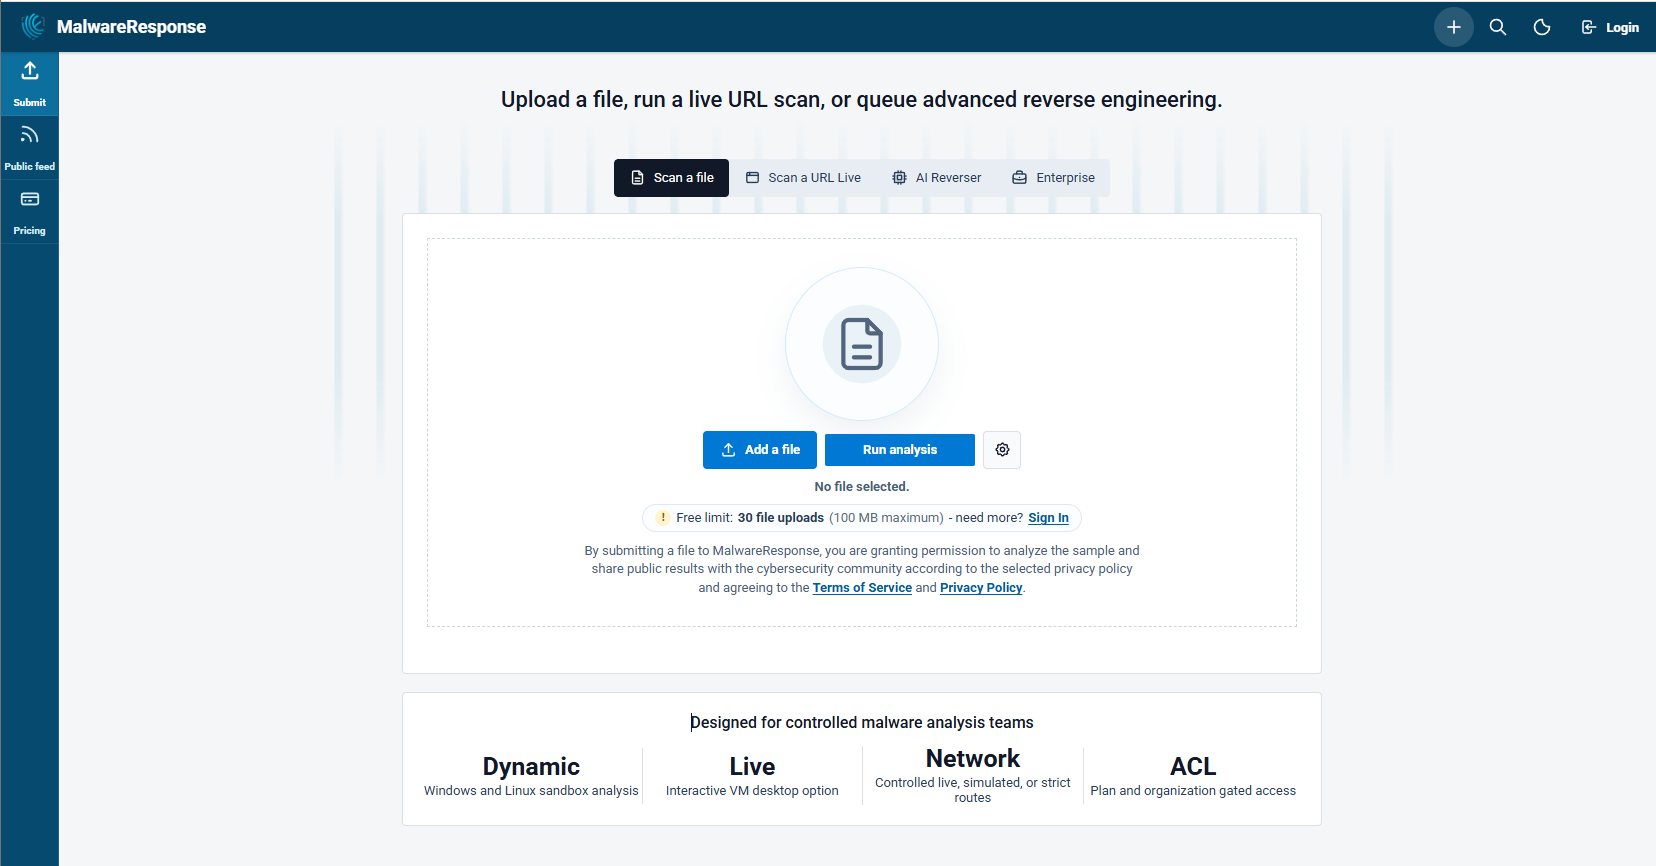
MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Discover
350 +

analysis workflows connected

Analyze files, URLs, and malware behavior with response-ready evidence visual

Turning malware and intelligence into response-ready evidence

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Discover
350 +

analysis workflows connected

Analyze files, URLs, and malware behavior with response-ready evidence visual

Analyze files, URLs, and malware behavior with.

Explore more
Analyze files, URLs, and malware behavior with response-ready evidence visual

MalwareResponse is the Emin Labs platform for suspicious files, URLs, sandbox behavior, extracted indicators, and response evidence. It.

Move from raw security signals to evidence, context, decisions, and durable detection improvements.

Analyze files, URLs, and malware behavior with response-ready evidence visual Analyze files, URLs, and malware behavior with response-ready evidence visual
  • 20K+ users
20 k+
live users
Analyze files, URLs, and malware behavior with response-ready evidence visual

Analyst support during malware response

Escalate suspicious samples, validate behavior, and receive practical containment and detection guidance.

Analyze files, URLs, and malware behavior with response-ready evidence visual
about

Use evidence, intelligence, and expert workflows to improve response

270 k
Security workflows for our clients

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

For SOC, CERT, MDR, MSSP, malware analysis, and incident response teams, MalwareResponse at www.malwareresponse.com connects suspicious artifacts to sandbox evidence, expert review, and response-ready reporting.

Explore More
Analyze files, URLs, and malware behavior with response-ready evidence visual

Evidence intake

Bring suspicious artifacts into one controlled workflow for SOC, MDR, MSSP, and incident response teams.

Analyze files, URLs, and malware behavior with response-ready evidence visual

Files, URLs, hashes, archives

Route files, URLs, hashes, archives, and phishing evidence into repeatable analysis queues.

Analyze files, URLs, and malware behavior with response-ready evidence visual

Behavior and context

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Analyze files, URLs, and malware behavior with response-ready evidence visual

Response-ready output

Export analyst-ready reports with verdicts, IOCs, confidence, containment notes, and detection guidance.

Emin Labs platform workflow

MalwareResponse connects sandbox evidence, analyst review, and response handoff in one workflow.

IBM QRadar integration logo
Splunk integration logo
SentinelOne integration logo
Proofpoint integration logo
ServiceNow integration logo
Slack integration logo

MalwareResponse overview

/ Malware evidence, IOC enrichment, and response handoff for security operations. / Malware evidence, IOC enrichment, and response handoff for security operations.
what we do

MalwareResponse turns suspicious files and URLs into response evidence

Submit suspicious files, URLs, hashes, and phishing artifacts into a controlled analysis workflow.

MalwareResponse combines automated sandbox evidence with expert review when a sample needs deeper analyst judgment.

  • File and URL detonation
  • Behavior evidence
  • IOC enrichment
  • Analyst review
  • Report-ready notes
  • SIEM, SOAR, EDR handoff
Explore More

Integrations for malware response workflows

Analyze files, URLs, and malware behavior with response-ready evidence visual
how it works

From suspicious artifact to decision, detection, and response

01

Submit evidence

Upload files, URLs, hashes, screenshots, or phishing artifacts from SOC, MDR, or incident response queues.

02

Analyze behavior

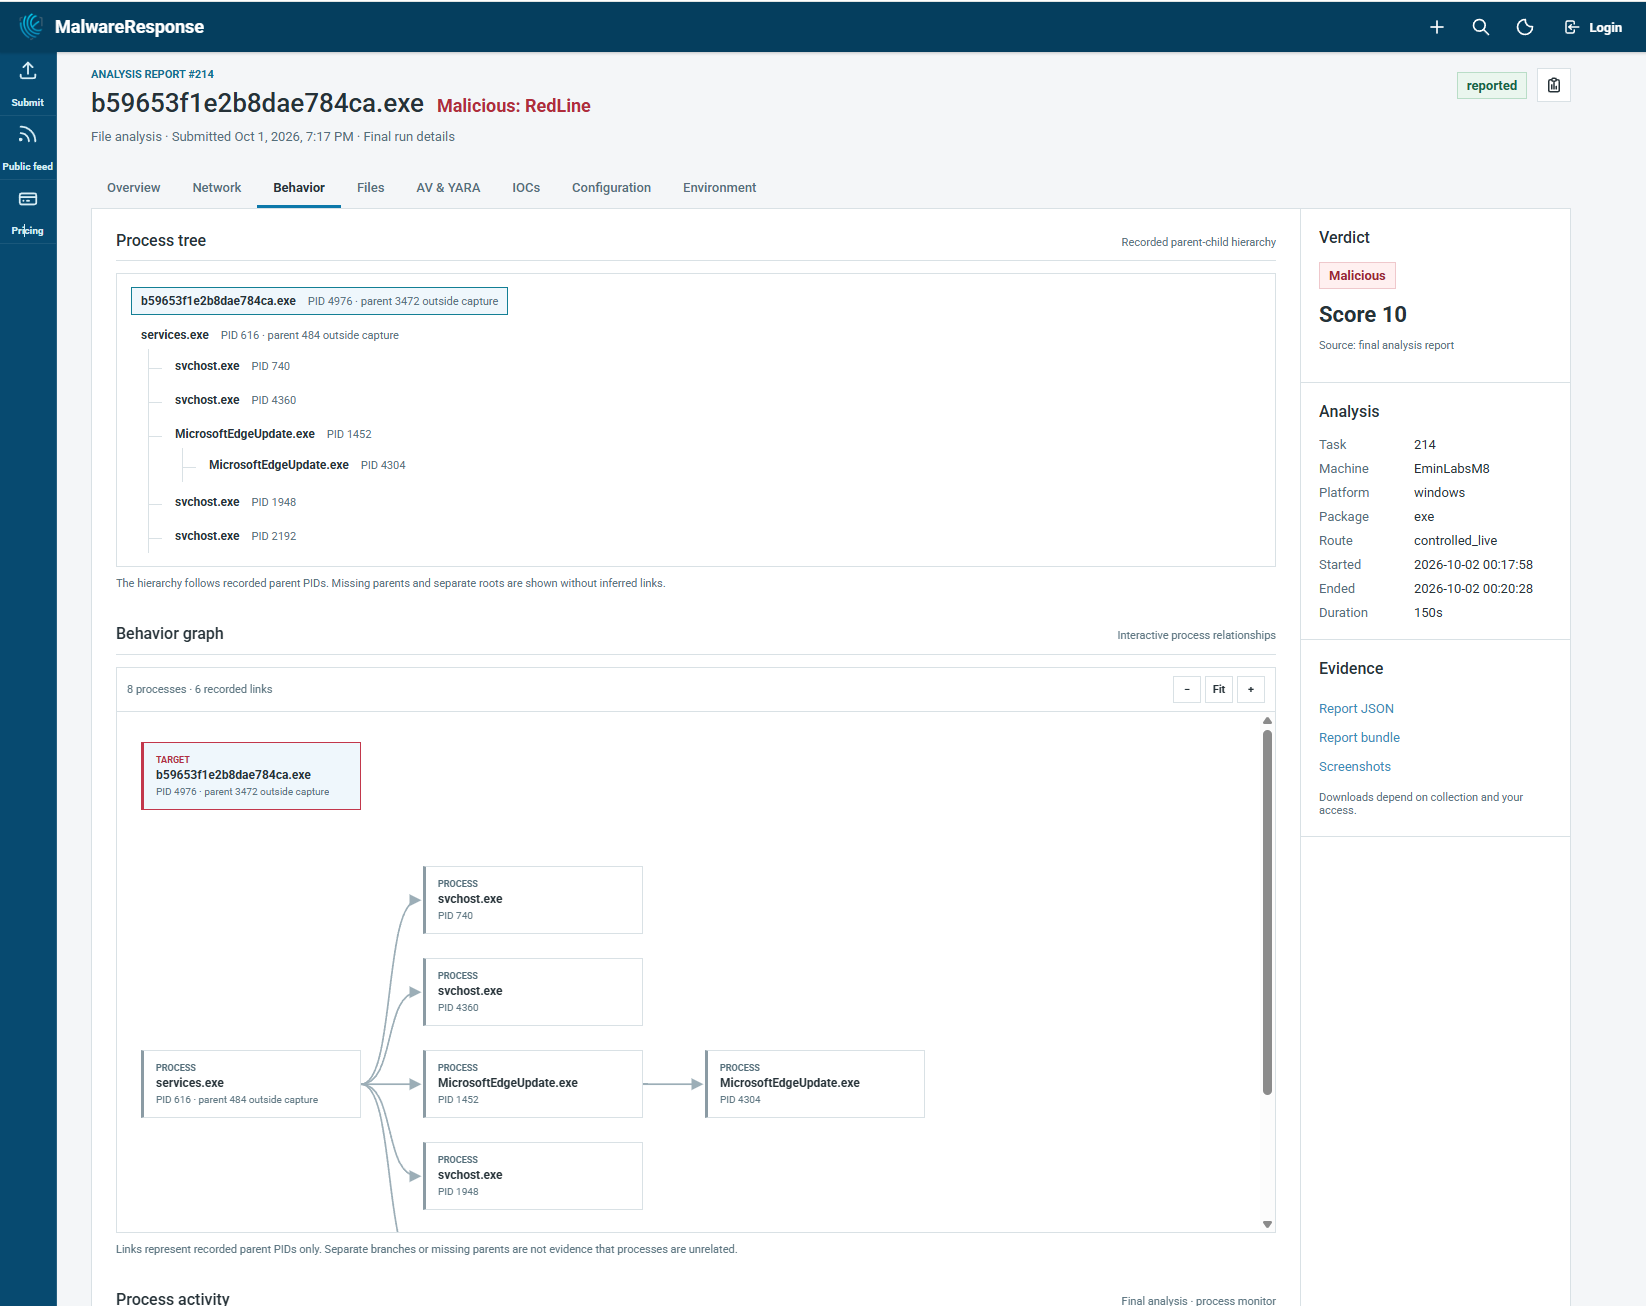
Detonate safely, capture process activity, network traffic, screenshots, dropped files, and suspicious behaviors.

03

Report and respond

Return verdicts, IOCs, confidence notes, ATT&CK context, and response guidance analysts can act on.

projects

Security workflows for malware analysis, intelligence, detection, and managed response

200 +
Projects
Workflow

Suspicious file and URL triage

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

Malware behavior evidence packs

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

IOC enrichment and ATT&CK mapping

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

Response handoff for SOC teams

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

Suspicious file and URL triage

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

Malware behavior evidence packs

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

IOC enrichment and ATT&CK mapping

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more
Workflow

Response handoff for SOC teams

Handle suspicious payloads and web chains from phishing, EDR, email, proxy, and SOC alert sources.

Explore more

Security teams use MalwareResponse to move from suspicious artifacts to response decisions.

SOC analyst 

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Incident responder

The reports are concise enough for response calls and detailed enough for detection engineering.

Threat intelligence lead

The evidence packs connect behavior, indicators, confidence, and response priorities in a format our analysts can use.

Malware researcher

The workflow gives our team a clear path from suspicious artifact to evidence-backed containment and detection notes.

Detection engineer

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Security operations lead

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

MSSP analyst

The analyst-ready reports help our team brief stakeholders without losing the technical detail responders need.

 CTI analyst

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Response lead

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

SOC analyst

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Platform user

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Regional security team 

MalwareResponse turns suspicious artifacts into sandbox evidence, IOC context, and response-ready reporting for security teams.

Analyze files, URLs, and malware behavior with response-ready evidence visual
blog

Exploring malware behavior, sandbox evidence, and response decisions with Emin Labs research

Analyze files, URLs, and malware behavior with response-ready evidence visual
24 AUG. 2024 / Emin Labs Research

From suspicious file to response-ready malware report

Practical notes on malware behavior, extracted indicators, and response decisions for security teams.

Analyze files, URLs, and malware behavior with response-ready evidence visual
24 AUG. 2024 / Emin Labs Research

How sandbox behavior supports faster incident response

Practical notes on malware behavior, extracted indicators, and response decisions for security teams.

partners

Our trusted collaborators in progress and success

Fastly integration logo
Fortinet integration logo
GitHub integration logo
Google GKE integration logo
IBM QRadar integration logo
Proofpoint integration logo
Qualys integration logo
SentinelOne integration logo
ServiceNow integration logo
Slack integration logo
Splunk integration logo
Thales integration logo

Elevate your business with our innovative solutions